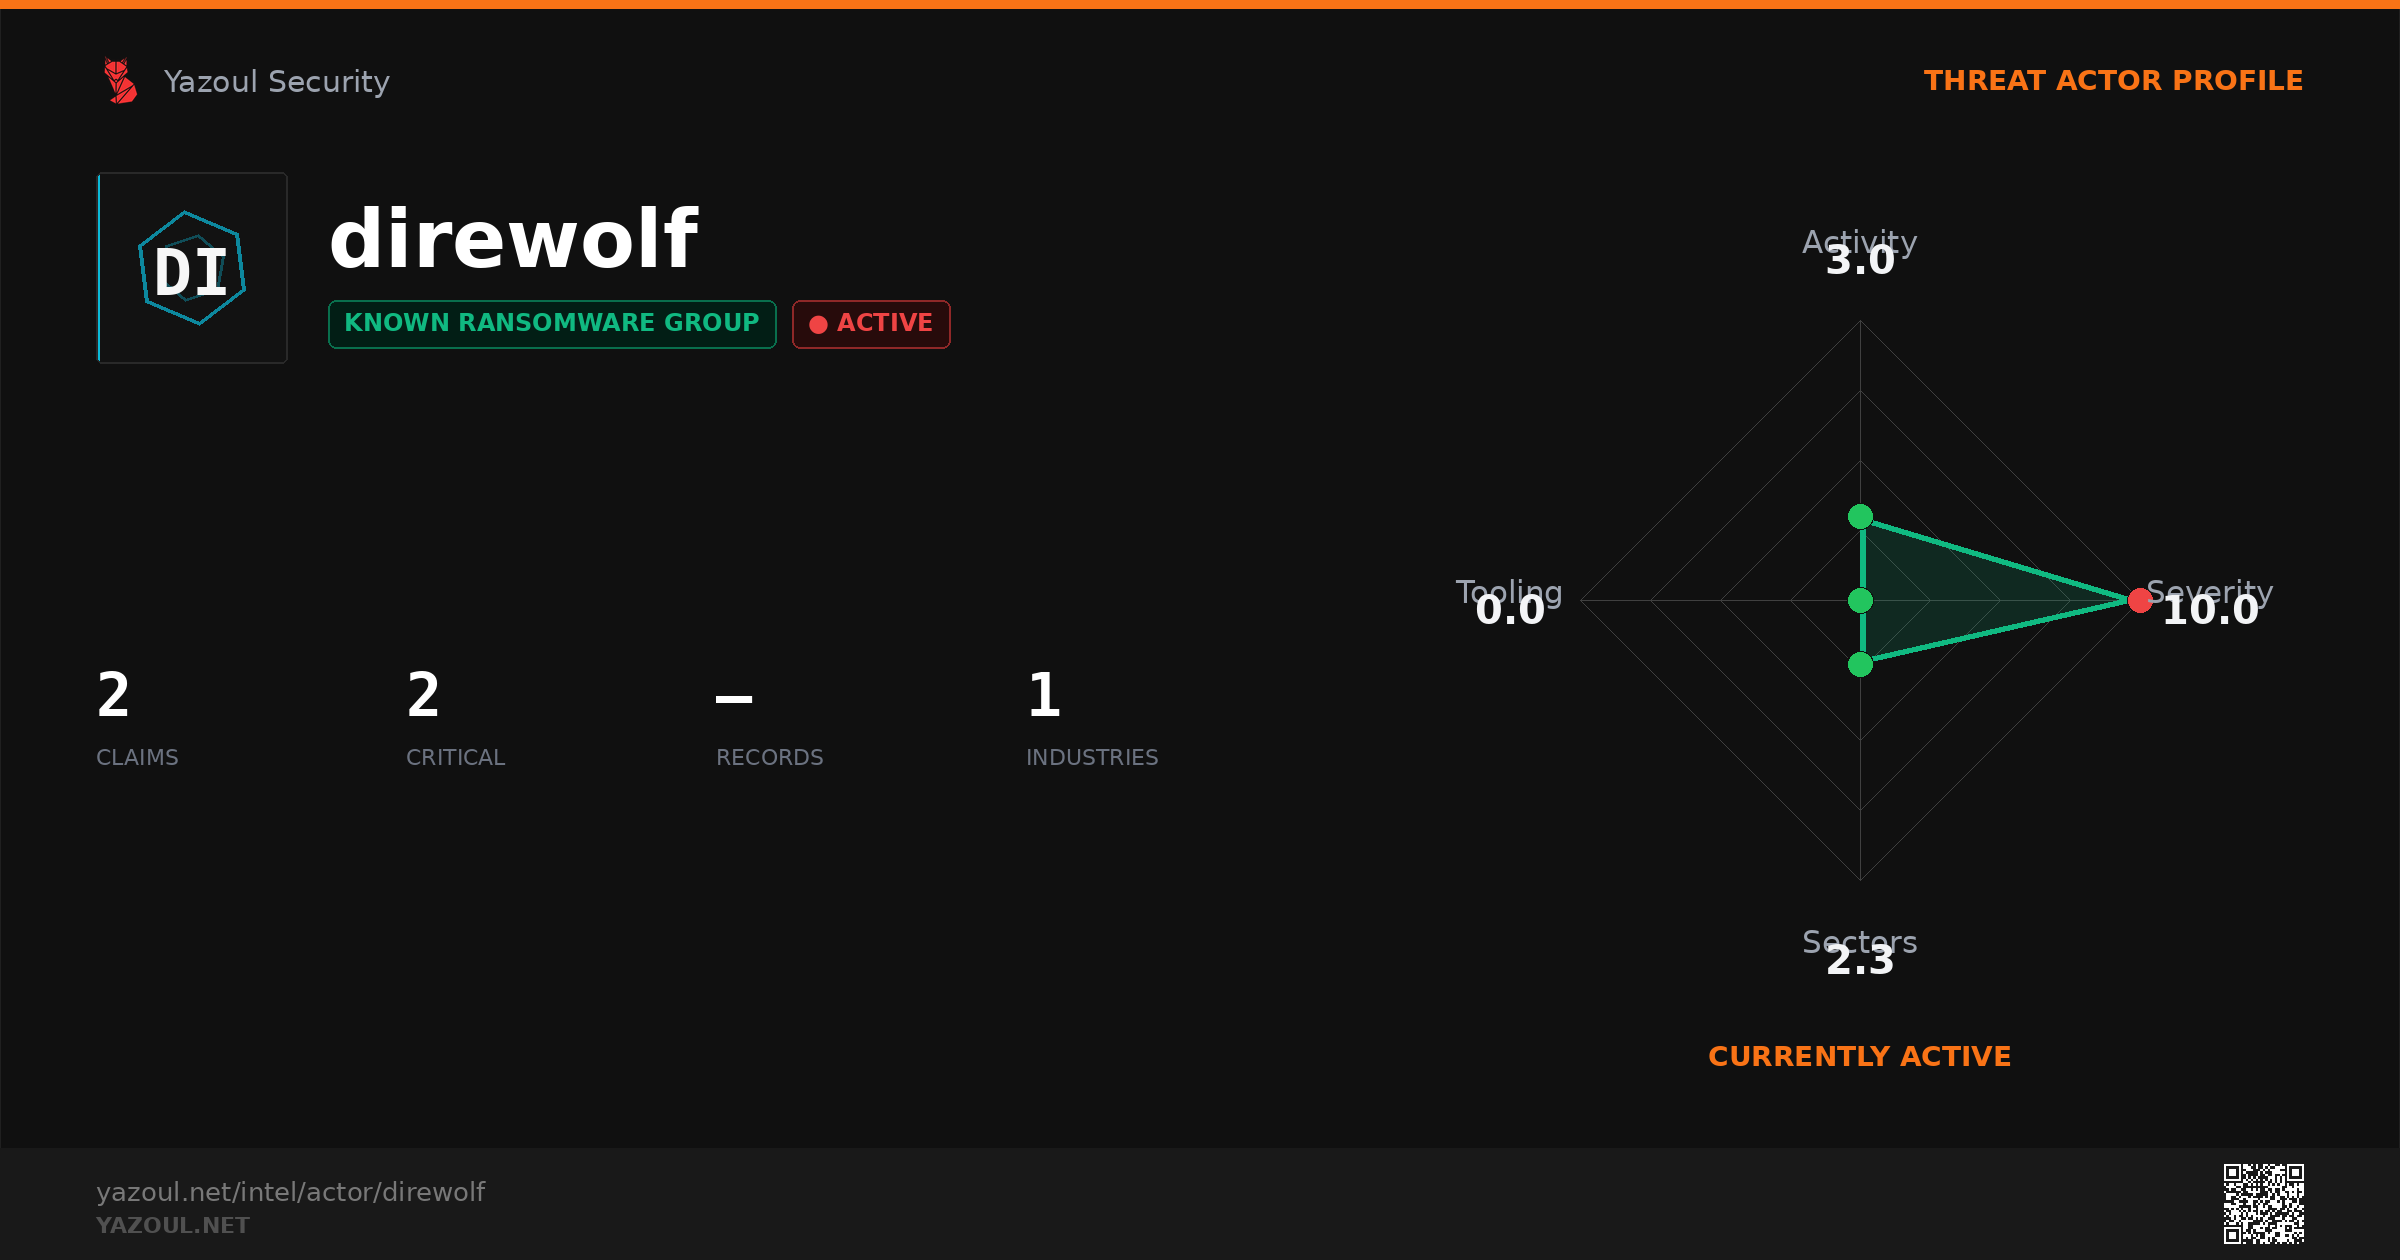
direwolf
Known ransomware group ACTIVE Currently active
Dire Wolf is a sophisticated human-operated ransomware group first documented in May 2025, written in Golang using Curve25519/ChaCha20 encryption, targeting manufacturing and technology sectors across 13+ countries with ransoms up to $500,000, operated by a tight core team rather than a broad affiliate program.
2
Total Claims
2
Critical
—
Records Claimed
1
Industries Hit
Active span: Sep 9, 2026 – Oct 13, 2026 · 2 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (1)Sep 2026
LessMore
Oct 2026Share this profile
Top Targeted Industries
Financial Services 2
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
1
Known leak sites