lockbit5
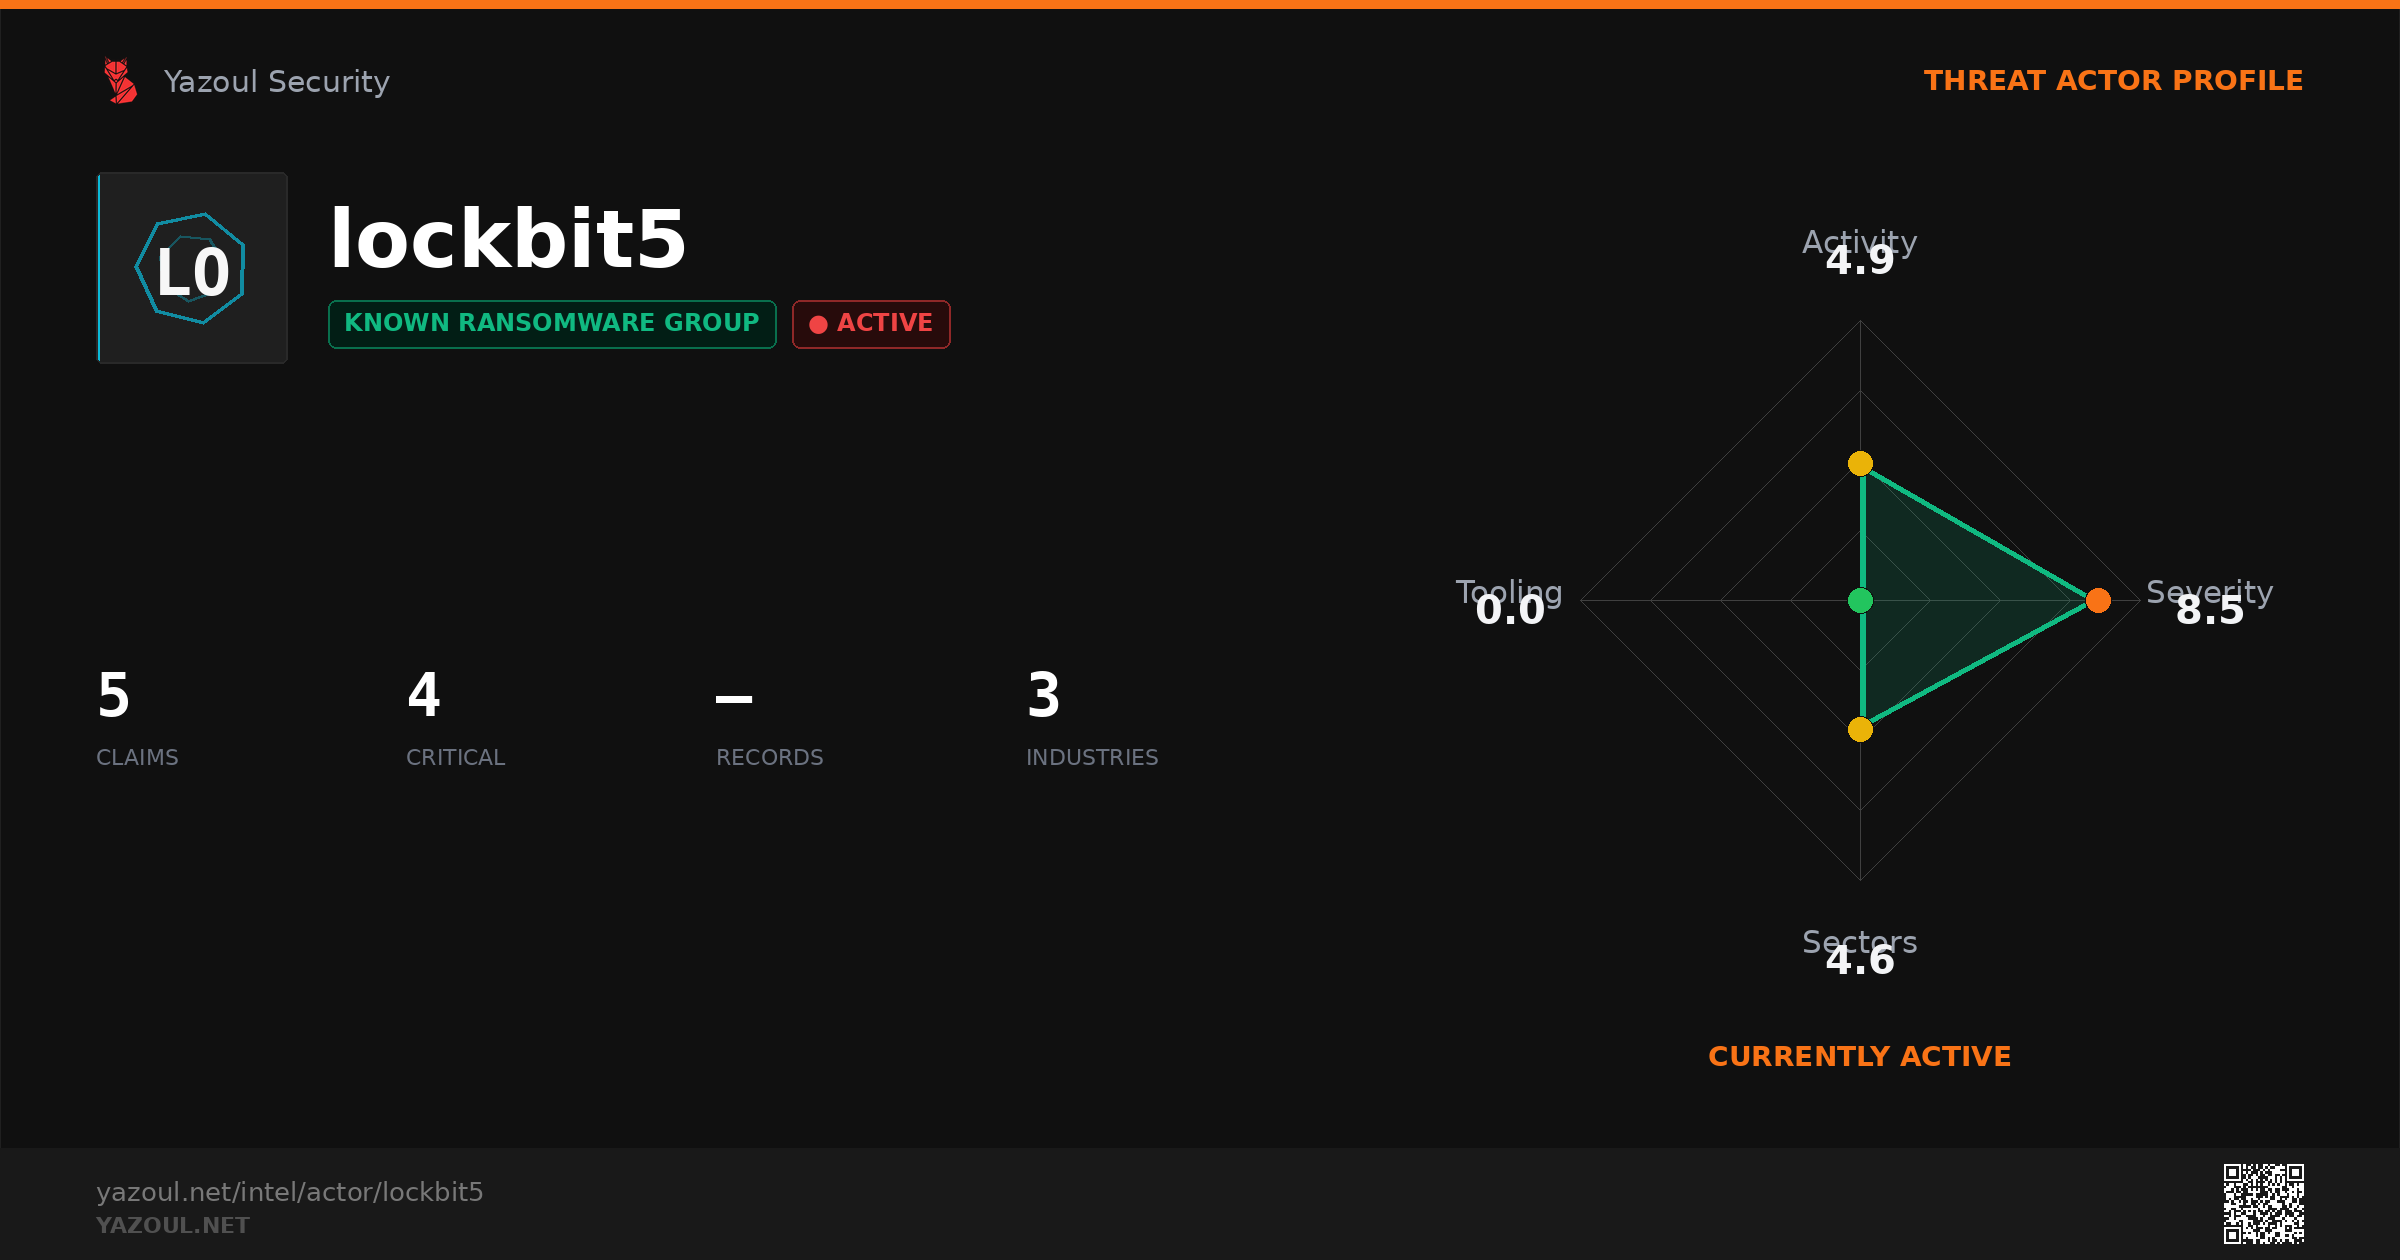
Known ransomware group ACTIVE Currently active
LockBit 5.0 ("ChuongDong") emerged in September 2025 as the group's resurgence following the February 2024 law enforcement takedown, introducing cross-platform payloads targeting Windows, Linux, and VMware ESXi with enhanced evasion capabilities and continuing the RaaS affiliate model of its predecessors.
5
Total Claims
4
Critical
—
Records Claimed
3
Industries Hit
Active span: Sep 9, 2026 – Sep 22, 2026 · 5 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (5)Sep 2026
LessMore
Sep 2026Share this profile
Top Targeted Industries
Healthcare 3
Financial Services 1
Government & Defense 1
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
23
Known leak sites
Targeted Organizations
Claims by lockbit5
Critical
Ransomware Claim: taspenlife.com
taspenlife.com
lockbit5
Ransomware Healthcare
Sep 25, 2026 Critical
Ransomware Claim: siinqeebank.com
siinqeebank.com
lockbit5
Ransomware Financial Services
Sep 21, 2026 Critical
Ransomware Claim: hygear.com
hygear.com
lockbit5
Ransomware Healthcare
Sep 19, 2026 Low
Ransomware Claim: comune.robeccosulnaviglio.mi.it
comune.robeccosulnaviglio.mi.it
lockbit5
Ransomware Government & Defense
Sep 14, 2026 Critical
Ransomware Claim: amorsaude.com.br
amorsaude.com.br
lockbit5
Ransomware Healthcare
Sep 11, 2026