metaencryptor
Known ransomware group ACTIVE Currently active
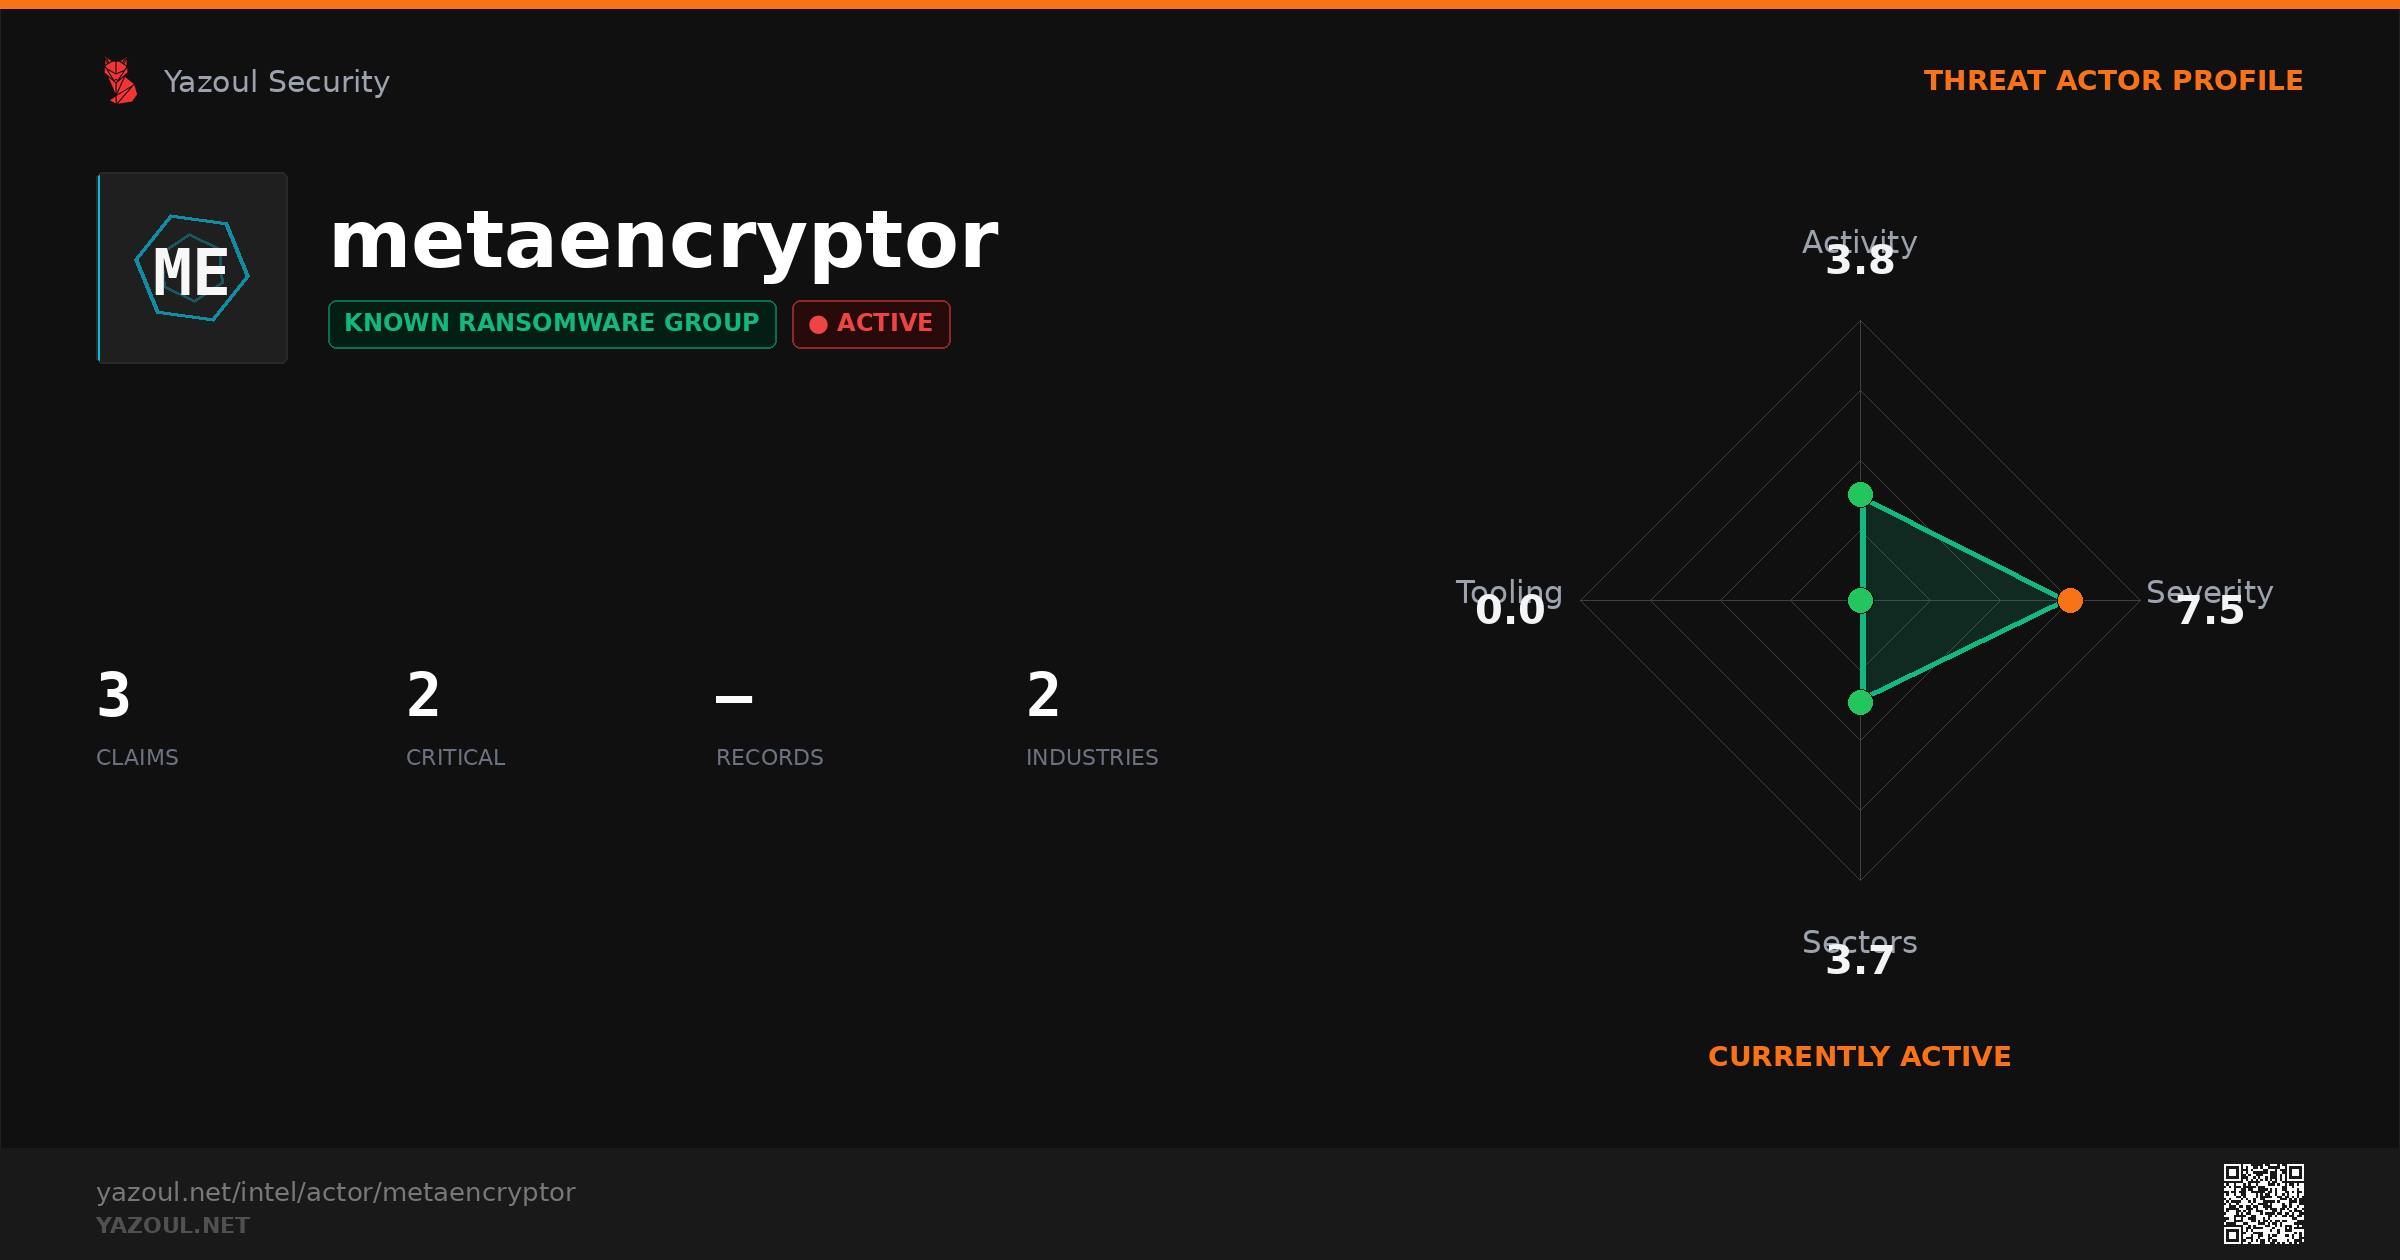
MetaEncryptor is a ransomware group first observed in mid-2023, targeting medium-to-large enterprises in legal, technology, logistics, manufacturing, and finance sectors primarily in the UK, Europe, and Southeast Asia, using AES-256/RSA-2048 encryption and double extortion.
3
Total Claims
2
Critical
—
Records Claimed
2
Industries Hit
Active span: Sep 21, 2026 – Sep 25, 2026 · 3 organizations targeted
Currently active
Actor Threat Profile
Activity Timeline
Peak: Sep 2026 (3)Sep 2026
LessMore
Sep 2026Share this profile
Top Targeted Industries
Healthcare 2
Energy & Utilities 1
Tradecraft & Infrastructure
0
Documented tools
0 / 0
MITRE tactics / techniques
2
Known leak sites
Targeted Organizations
Claims by metaencryptor
Critical
Ransomware Claim: Platinum Healthcare Staffing
Platinum Healthcare Staffing
metaencryptor
Ransomware Healthcare
Sep 26, 2026 Low
Ransomware Claim: GE Vernova Inc.
GE Vernova Inc.
metaencryptor
Ransomware Energy & Utilities
Sep 26, 2026 Critical
Ransomware Claim: Hudson MD Group, LLC
Hudson MD Group, LLC
metaencryptor
Ransomware Healthcare
Sep 21, 2026